Inside Zetta · Information security
The mechanic finally fixed his own car
Zetta is now certified to ISO/IEC 27001:2022. Here is what two years of work actually involved, who did it, and what it changes for the businesses we look after.
That is an uncomfortable thing for an IT provider to say out loud. It was also true, and saying it out loud is what started the work.
On 4 August 2026, Sensiba Australia Pty Ltd certified Zetta’s information security management system against ISO/IEC 27001:2022. This is the story of what sat behind that certificate, because the certificate itself is the least interesting part.
What ISO 27001 actually asks of you
ISO 27001 is the international standard for information security management. It is not a scan, a product, or a badge you buy. It asks you to build a management system: to know what information you hold, understand the risks to it, decide which controls apply, prove those controls run, and then keep proving it.
Independent auditors test the whole thing. If the evidence is not there, the certificate is not either.
What the work involved
The honest summary is that it touched almost everything about how we operate.
We wrote and reviewed an entire policy suite. We ran a formal risk assessment and a risk treatment plan. We rolled management agents across the whole device fleet, tightened access, and closed gaps that had been quietly tolerated for years. We trained the team, gathered evidence, and then audited ourselves before anyone else could.
We did all of it while the day job carried on. No customer project was paused so we could go and get certified.
The toolset mattered
All 185 controls sit in Drata, our governance platform. That is not a footnote. Evidence collection is where most certification attempts quietly fall over: someone screenshots a setting, drops it in a folder, and eleven months later nobody can prove the control still runs.
Drata monitors the controls continuously rather than at audit time, which meant the Stage 2 audit ran through its audit hub instead of through a shared drive full of PDFs. Our auditors sampled evidence directly. Three days, remote, no scramble.
How it ran, month by month
Fix the fundamentals
An internal device management overhaul led by Ross Craven and the service desk team. Every Zetta-owned device brought under consistent management, with an accurate asset record to match.
Risk assessment
A formal assessment of what information we hold, where it lives, and what could go wrong with it.
Risk treatment plan
Decisions on what to fix, what to accept, and who owns each one.
Policies, internal audit, management review
The information security policy and Statement of Applicability signed off, an internal audit completed, and leadership formally reviewing the system rather than nodding at it.
Stage 2 audit
Three days with Sensiba's audit team, run through the Drata audit hub. Walkthroughs, evidence sampling, and a lot of very specific questions.
Certified
Certificate 202608-295 issued, valid to 4 August 2029, with annual surveillance audits in between.
Simon led it
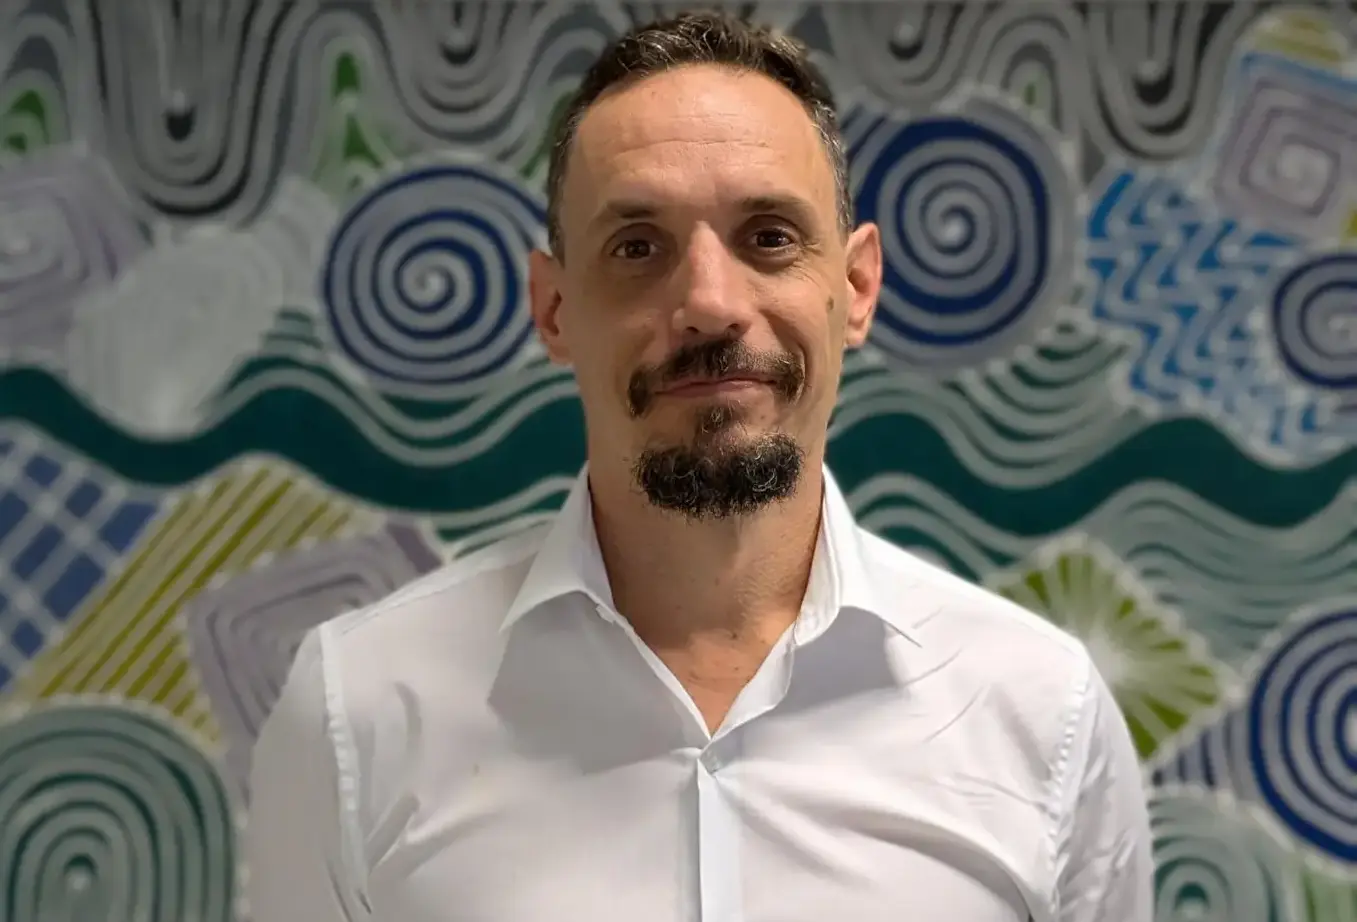
Certifications like this usually have one person who carries them, and for us that was Simon Bendotti, our Operational Services Manager.
Simon owned the management system end to end: the scope, the policy suite, the risk work, the evidence base, and the unglamorous business of chasing people for the one document nobody could find. When the Stage 2 audit came around, he was the person in the room for three days answering an auditor’s questions about controls he had personally put in place.
"It started as a very daunting task, but we methodically worked through it, all while staying focused on delivering for our customers. There's something genuinely special about a small team rallying around a big goal and actually pulling it off."
Simon Bendotti, Operational Services Manager
It was not a solo effort
Simon is quick to point out that the work was shared. Rodrigo Bonhin, Arun Chaudhary, Amy Hearn and Thales Quintas carried large parts of it, alongside the earlier infrastructure work from Ross Craven and the service desk crew.
That is a small group of people to put a whole management system on. They did it around their existing workloads, and the certificate belongs to them as much as to the company.
What the certificate does and does not say
- Certified entity
- Zetta Pty Ltd, Level 11, 108 St Georges Terrace, Perth WA 6000
- Standard
- ISO/IEC 27001:2022, information security management system
- Certification body
- Sensiba Australia Pty Ltd
- Certificate number
- 202608-295, issued 4 August 2026, expiring 4 August 2029
- Scope
- The information security management system of Zetta Pty Ltd company IT services, including operations and delivery, where information assets are managed by Zetta.
Worth being precise about this, because certification language gets stretched. ISO 27001 certifies a management system, not a product and not a promise that nothing will ever go wrong. What it does say is that an accredited third party looked at how we manage information security, sampled the evidence, and found it conformed to the standard.
It is also not a finish line. Surveillance audits run annually, and recertification comes around in three years. A system you stop maintaining stops being certified.
What this means if you work with us
Independent proof, not assurances
Your information is handled inside a system that an accredited auditor has tested. That is a different thing from a vendor telling you they take security seriously.
Easier procurement
If your tenders, insurers or board ask for evidence of an IT partner’s security posture, the certificate answers it directly.
We have done it, so we can help you do it
The frameworks, the toolset and the discipline are now things we have lived through, not things we have read about. It is the same Drata platform behind our Managed Security Governance service.
Habits that outlast the audit
Access reviews, change control, evidence trails and risk registers are now simply how we operate, which is the part that actually protects your data.
If you are looking at ISO 27001, Essential Eight or a security uplift of your own and want to talk to someone who has recently been through the messy middle of it, we are happy to share what we learned. Including the parts we would do differently.
Work with us
Talk security with a certified team
Perth-based, WA-owned since 2004, and now certified to ISO/IEC 27001:2022.
Acknowledgement of Country
Zetta acknowledges the Whadjuk people of the Noongar nation, the Traditional Custodians of the land on which we live and work, and pays respect to Elders past and present.